TL;DR
- In the agentic development lifecycle (ADLC), AI agents plan, build, test, and ship software by acting directly in your repos, tools, and pipelines, not just suggesting code.
- Agents add risk at three points: insecure code and design flaws by default, hallucinated or unvetted dependencies (only 1 in 5 AI-recommended dependency versions are safe), and actions taken with the developer’s own permissions before any code reaches review.
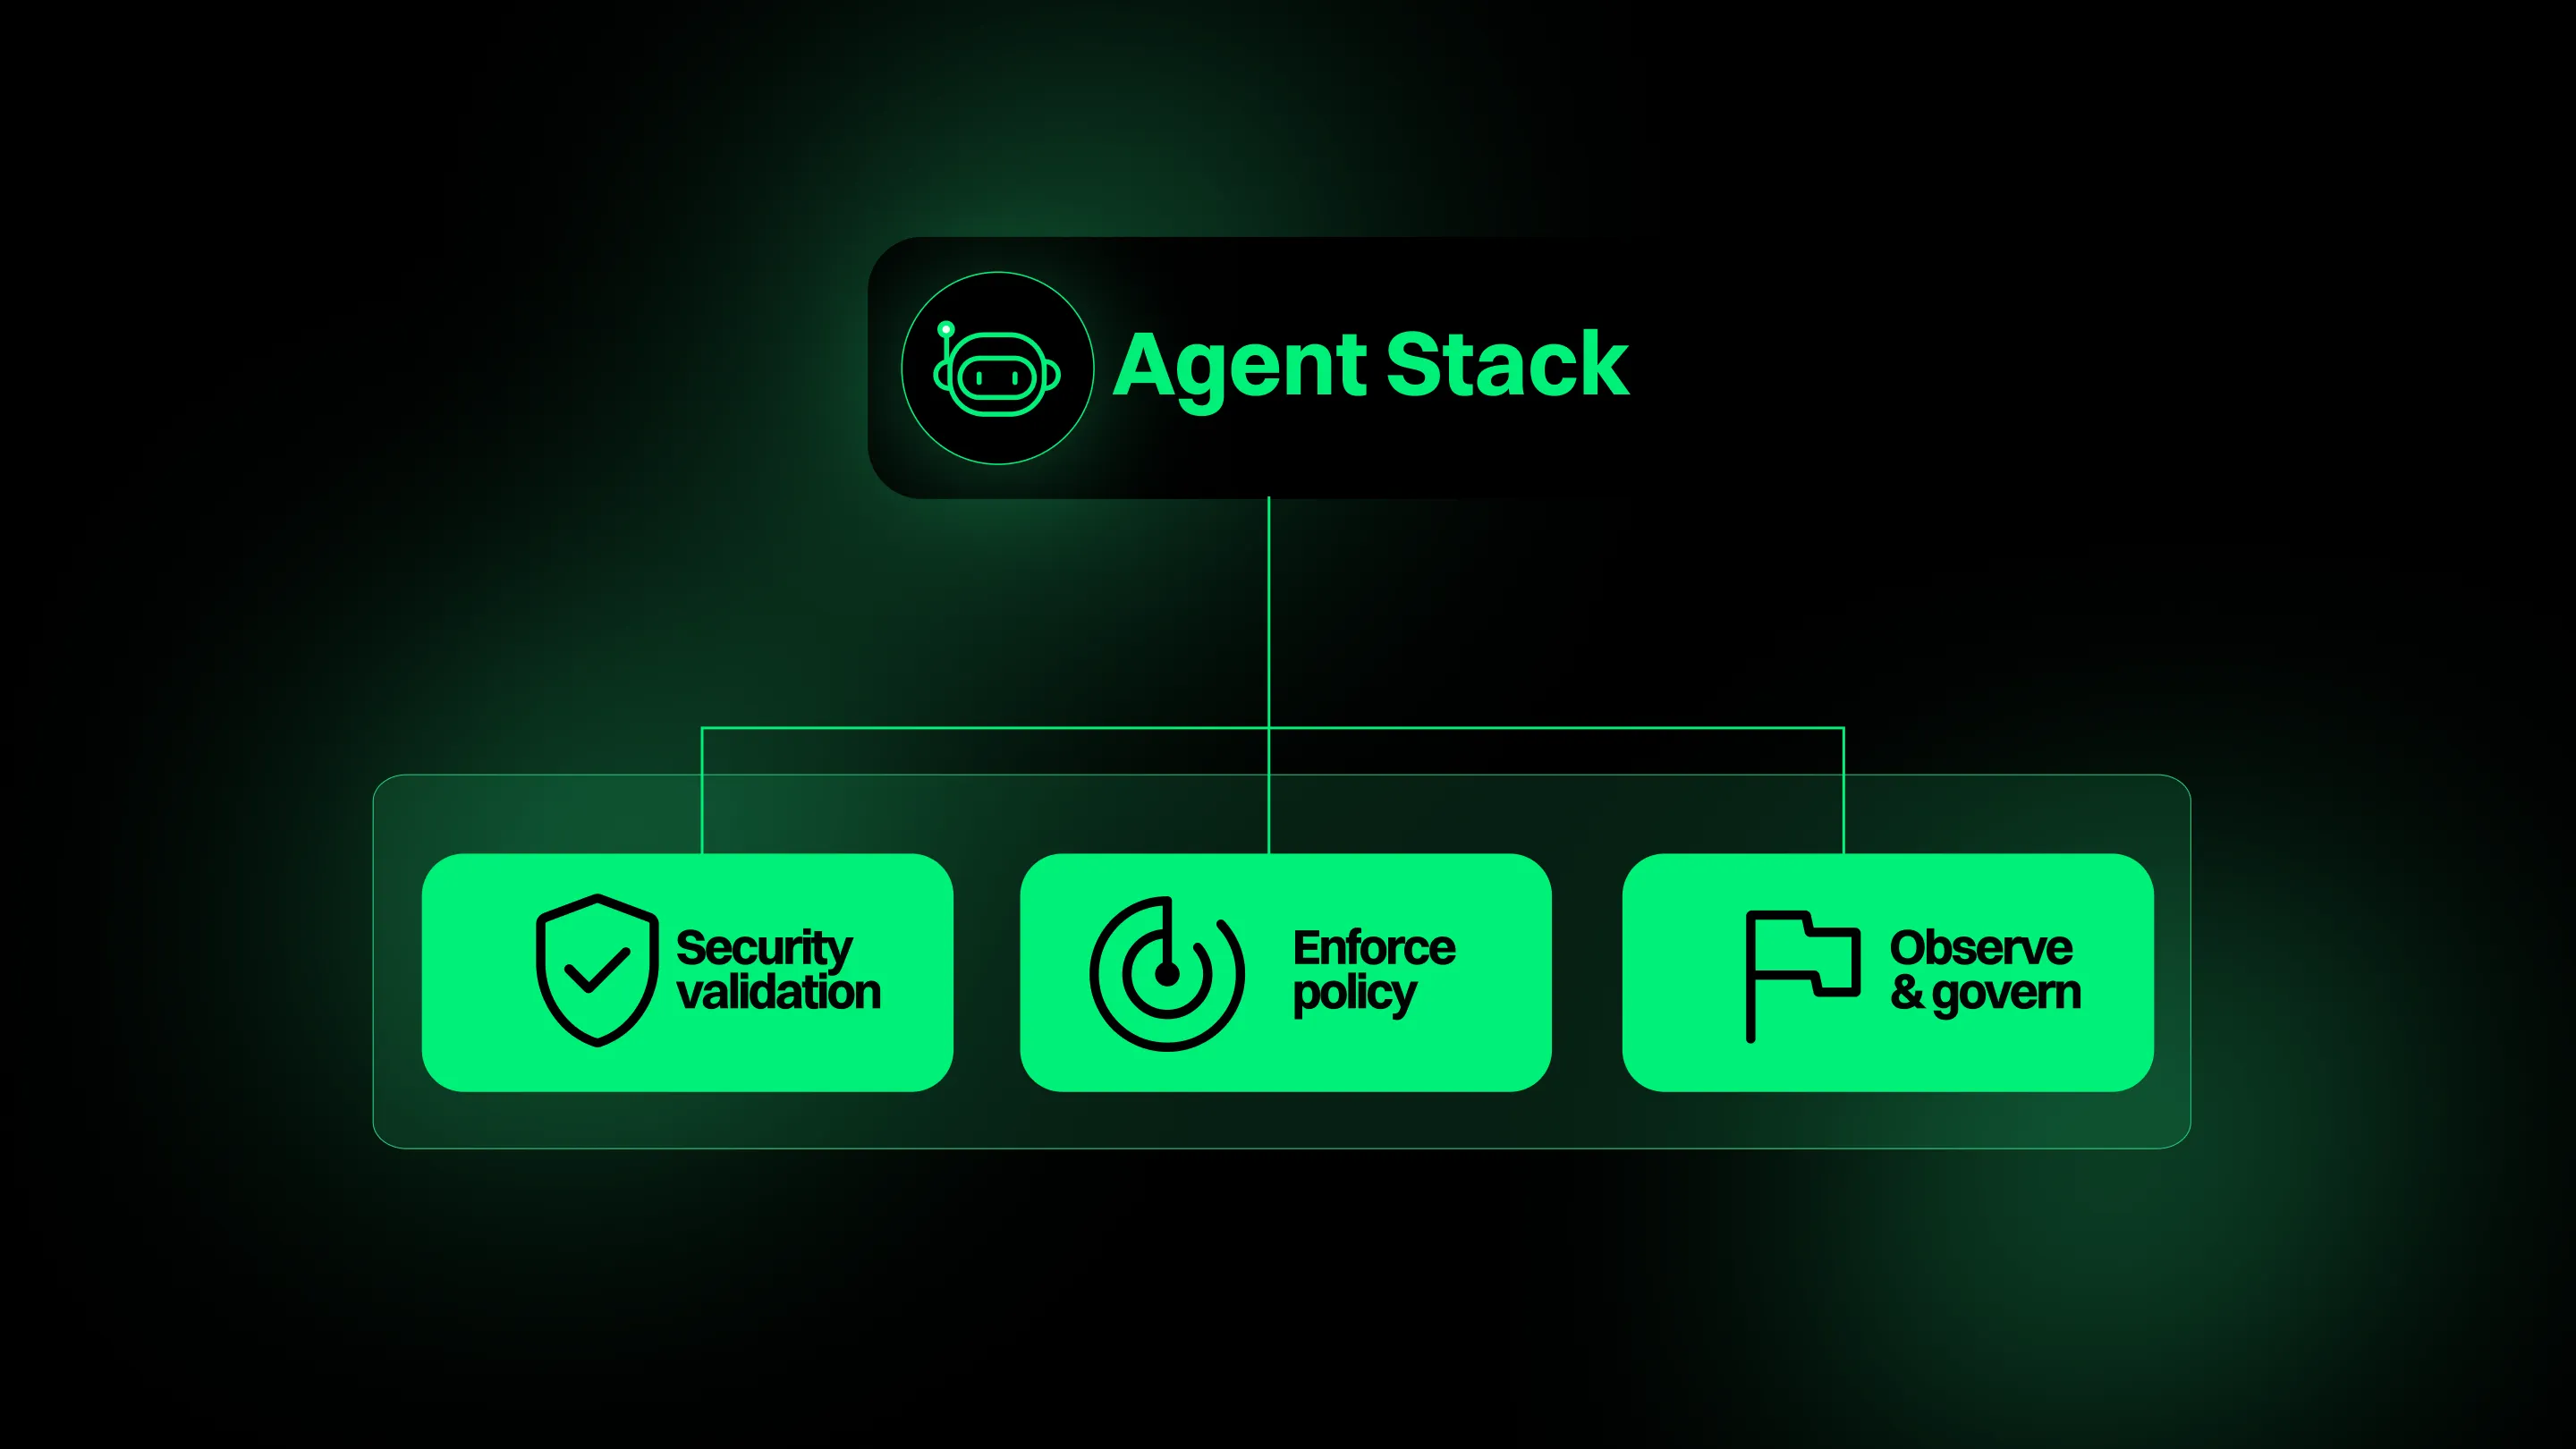
- A secure ADLC has two layers: govern what agents can access, run, and install, and independently verify the code and dependencies they produce. Either layer alone leaves a gap.
- Controls have to run at agent speed. Block risky packages at install time, review every PR for security impact, and prioritize findings by reachability so review keeps pace without stalling delivery.
Trace a change backward from production. The commit, the review, the tests, the dependency it pulled in, the prompt that started it. A person used to sit at every step in that chain. In the agentic development lifecycle (ADLC), they often sit at only one.
A secure ADLC puts controls back into that chain. It does two jobs at once: it limits what coding agents are allowed to do, and it independently checks everything they produce. This guide covers what the ADLC is, how it changes the Software Development Lifecycle (SDLC), where the new risks come from, and the controls to apply at each stage.
ADLC Definition: What is the agentic development lifecycle (ADLC)?
The agentic development lifecycle is the process by which AI agents plan, build, modify, test, and ship software by working directly with tools, codebases, APIs, and development environments. Agents act across the toolset instead of just suggesting code.
A secure agentic development lifecycle places controls at each of those steps. Some controls govern the agent itself: what it can access, run, and install. Others verify the code, dependencies, and artifacts it creates before they reach production. Done well, neither layer slows the agent down.
This is a real shift from autocomplete. An agent does not suggest a line and wait. It reads the repo, edits many files, installs packages, runs tests, and opens a pull request while you watch.
Two meanings of "ADLC"
You will see the acronym used two ways, and the security guidance differs for each.
This guide is about the first meaning: agents as members of your engineering team. If you are building agents as a product, many of the controls overlap, but the lifecycle stages differ.
Why it matters now
In the 2026 Stack Overflow Developer Survey, coding assistants and agents became the most common way developers use AI, and 73% of respondents now use them daily. Jellyfish, analyzing 20 million pull requests across 200,000 engineers, found 64% of companies now generate a majority of their code with AI assistance. Fully autonomous agent activity, where an agent opens the pull request start to finish, is still a small share of that dataset but is growing fast.
That last trend is the one to plan around. The goal is not to slow agents down. It is to keep their speed while making sure what ships is safe, which means controls that run at agent speed rather than gates that stall it.
Agentic development vs. AI-assisted coding
The difference is who's driving. An AI assistant suggests code, and a human accepts or rejects it. An agent takes action across tools, repos, and the pipeline, then presents finished work.
That difference changes the risk model. When a human writes every line, review scales with people. When an agent opens dozens of pull requests a day, the old one-reviewer-per-change ratio breaks.
ADLC vs. SDLC: what changes for security?
The agentic development lifecycle does not replace the software development lifecycle (SDLC). Requirements, design, code review, testing, and secure release practices all still apply. What changes is who is acting inside the lifecycle and what they are allowed to do.
In a traditional SDLC, security controls assume a human author. Developers have identities, review is human-paced, and a person decides which package to install or which command to run. In the ADLC, an agent makes many of those decisions, often using the same credentials and access as the developer who launched it.
That creates three new responsibilities for security teams:
- Govern agent identity and permissions. Know which agents are running, whose access they use, and what they can touch.
- Govern agent actions. Decide which tools, MCP servers, commands, and package sources an agent may use, and which actions need a human to approve them.
- Verify agent output independently. Treat agent-generated code and dependencies like any untrusted contribution. Don't rely on the agent's own claim that its work is safe.
The other shift is timing. In many SDLC programs, security shows up as a checkpoint late in the pipeline. At agent speed, a late gate either blocks everything or gets bypassed. A secure ADLC moves security guidance into the workflow itself, so agents get feedback while they work, not after the pull request is open.
Where the agentic development lifecycle creates new security risk
Agent speed multiplies familiar security problems and adds new ones. The core issue isn't a single bad line of code. It's volume plus autonomy outrunning the review that used to catch mistakes, and agents taking actions no one reviews at all.
Insecure code, by default
Agents learn from public code, so they repeat the insecure patterns in it. That includes missing input validation, injection, broken authentication, and hardcoded secrets. The benchmarks back this up.
On the BaxBench benchmark, 62% of the solutions generated even by the best model are either incorrect or insecure. In one 2026 benchmark, 61% of solutions from SWE-Agent with Claude 4 Sonnet were functionally correct, but only 10.5% were secure, so most correct solutions still had security problems.
A harder problem is the design flaw: a security weakness in how the code is structured, not a single risky function. Picture an agent that adds a working feature but routes it around your existing permission checks. Endor Labs research on architectural design flaws found these often pass static analysis, because the code looks correct line by line. For a full list, see the Endor Labs breakdown of common AI code vulnerabilities.
Hallucinated and unvetted dependencies
Agents pull in packages on their own, and they don't always pick safe ones. A hallucinated dependency is a package an agent recommends that doesn't actually exist. Attackers can register that predicted name later and wait for installs.
Our State of Dependency Management research found that only 1 in 5 AI-recommended dependency versions are safe. It also found 49% carry known vulnerabilities, and 34% are hallucinated (they don't exist).
The blast radius is wide because of transitive dependencies, meaning the dependencies pulled in by your dependencies. One package an agent adds can quietly bring dozens more into your build.
Agent actions: commands, tools, MCP servers, and inherited permissions
This is the risk a code scanner never sees. To finish a task, a coding agent may run shell commands, execute scripts, install packages, edit configuration, and call external tools. It usually does all of this with the developer's own access: their repos, their cloud credentials, their tokens.
Agents increasingly reach for MCP servers. An MCP (Model Context Protocol) server is a connector that gives an AI agent access to external tools and data. The same Endor Labs research found 75% of MCP servers are built by individuals, and 82% use sensitive APIs. An unvetted MCP server or tool sits inside the agent's trust boundary, with the agent's permissions.
The result: an agent can do something risky (install a malicious package, read a secrets file, push to a protected branch) before any code reaches a pull request. Securing only the output misses this entire layer.
The verification gap: review can't keep pace
When agents ship code faster than people can read it, more changes go out unchecked. Faros AI telemetry shows pull requests merged without any review, human or agentic, are up 31.3% (a correlation, not proven causation).
The rate of new findings climbs too. Research cited by the Cloud Security Alliance found AI-assisted developers produce commits at three to four times the rate of their peers but introduce security findings at 10x the rate. And one 470-PR analysis found security issues were up to 2.74x higher in AI-co-authored pull requests, a sign of more security issues slipping through.
Developers already sense the problem. In the 2026 Stack Overflow Developer Survey, 48% of respondents said they trust AI output only when they can easily verify it, and just 16% trust it for most tasks short of important decisions. When agents produce more than people can check, verification has to be built into the workflow rather than left to the reader.
Speed you can't verify turns into security debt you pay for later.
Why traditional AppSec checkpoints fall short
Rule-based SAST (static application security testing) and SCA (software composition analysis) tools do their job well. They catch known anti-patterns and known CVEs (Common Vulnerabilities and Exposures). They struggle with what agents actually produce, and they don't see what agents do.
- Phantom and transitive dependencies get missed, because scanners often look at what you declared, not everything the build resolves.
- Design flaws pass, because each file reads as correct on its own.
- Agent actions are invisible, because a command run or a package installed on a workstation never reaches a pipeline scanner.
Manual review isn't a fix either. Reviewing every AI pull request by hand does not scale. The Endor Labs analysis of the cost of manual review shows reviewer hours climb faster than headcount ever could.
What makes an agentic development lifecycle secure?
A secure ADLC rests on one principle: constrain what agents can do, and independently verify what they produce. Either layer alone leaves a gap.
Teams that only scan output assume the agent behaved well on the way there. Teams that only lock down agent permissions assume a well-behaved agent writes secure code. Neither is true. The agent can install a malicious package that never shows up in a diff, and a fully sandboxed agent can still write an endpoint without authentication.
Think of the first layer as a security harness around the agent: it bounds what the agent can do, the same way you bound what a new contractor can access on day one. The second layer is the independent check: no change ships on the agent's word alone.
Security controls across the agentic development lifecycle
The stages below are an operating model, not an official standard. Teams name and split them differently, and frameworks such as NIST SP 800-218A map secure practices onto existing development processes rather than prescribing a fixed agentic phase list. Use the stages to check that every point where an agent acts has a matching control.
Stages 2 and 4 are where most programs have no control today. They are also where an agent can do damage before a single line reaches review.
How to put ADLC security controls in place
Agentic development security happens at the lifecycle's control points, not by bolting a separate "AI review" onto the end. Standards point the same way. NIST SP 800-218A extends secure development practices to generative AI. The Cloud Security Alliance has published guidance mapping controls for agentic development from design through operations, and OWASP catalogs the risks. The steps below turn that guidance into a control stack you can run, starting with the agent itself.
For step-by-step implementation, including hook policies, install-time package checks, and a worked example, see our guide to ADLC security best practices.
Govern what agents can do
You can't secure activity you can't see. Start by inventorying which agents run, who launches them, which tools and MCP servers they connect to, and what they change. Then apply coding agent governance: one consistent policy across the tools teams already use, such as Cursor, Claude Code, GitHub, and GitLab.
The coding-agent market is consolidating fast. In the 2026 Stack Overflow Developer Survey, Claude Code (66%) and GitHub Copilot (59%) were the most widely used coding agents, so most teams can start their inventory with the agents developers already have.
The core controls:
- Least privilege. Give agents scoped credentials for the task, not the developer's full access. Keep production secrets out of agent environments.
- Approved tools and MCP servers. Allow known, vetted tools and MCP servers. Block or flag the rest.
- Constrained execution. Define which commands and scripts an agent may run without asking, and which it may not run at all.
- Human approval for sensitive actions. Require a person to approve irreversible or high-impact actions, such as pushing to protected branches, changing CI configuration, or touching auth code.
- Auditability. Record what each agent did, with which permissions, so you can trace a change from prompt to production.
For how hook events, inventory, and policies connect in practice, see how agent governance policies work.
Stop risky packages before they install
Dependency risk starts the moment an agent runs an install command, long before a pull request exists. A package firewall checks each package at install time and blocks risky packages before installation, including known malware and names that look like hallucinated or typosquatted packages. This closes the gap that output-only scanning leaves open.
Prevent insecure patterns at generation
The cheapest fix is the code an agent never writes wrong. The Endor Labs approach to securing code at the source pushes security context into the agent and the IDE (integrated development environment). That steers agents away from insecure patterns before the code exists.
Prompt design helps more than people expect. Our research on safer prompting patterns found a recursive "secure-insecure diff" prompt pattern cut security-weakness density in generated Python by 77.5%.
Review every pull request for security impact
Every agent-generated pull request needs a review that understands architecture, not just patterns. Endor Labs' AI Security Code Review uses three agents on each change, acting as a developer, an architect, and a security engineer.
That mix catches design flaws rule-based scanners miss, like a new API endpoint added without authentication. A pattern scanner sees valid code. A reviewer that understands the app sees a missing check. Human code and agent code should meet the same bar.
Prioritize by reachability to cut the noise
Review keeps pace only when you cut findings down to what's actually exploitable. Reachability answers a plain question: does your code actually call the vulnerable function? The Endor Labs work on reachability-based dependency analysis builds a call graph to check that.
Full-stack reachability extends the same question across first-party code, open source dependencies, and container images, and attaches the evidence to each finding. Endor Labs data shows about 95% of vulnerabilities live in transitive dependencies, and only about 12% of a package's code is typically used. Because of that, reachability can cut the vulnerabilities that need remediation by up to 80%, and Endor Labs cuts noise by up to 95% using full-stack reachability.
Remediate without slowing delivery
Fixing should feel fast, not like a tax on shipping. Evidence-based remediation, safe upgrade paths, and backported patches let teams fix a CVE now and upgrade on their own timeline. Endor Labs customers see 83% fewer blocked pull requests and fix CVEs 6x faster.
The developer impact is the point. Teams get fewer interrupted pull requests, less time arguing about findings, and fixes that don't break the build. Consistent policy across agent and human work also gives compliance teams a clean story that maps to NIST, CSA, and OWASP guidance.
A secure ADLC workflow in practice
Here is how the two control layers work together on one ordinary task.
A developer asks a coding agent to add CSV export to a reporting service. Partway through, the agent decides it needs a parsing library and runs an install command. The package name it chose doesn't exist on the registry yet, a classic hallucination. Worse, someone registered a similar name last week.
- Prevent. The package firewall checks the install request, flags the package as new and suspicious, and blocks it. The agent gets that feedback in the session and picks a well-established library instead. Nothing malicious ever touches the workstation.
- Constrain. While wiring up the feature, the agent tries to edit the service's CI configuration to add a build step. Policy marks CI changes as sensitive, so the action pauses for the developer to approve or deny.
- Verify independently. The agent opens a pull request. Security-aware review notices that the new export endpoint skips the permission check the other report endpoints use, a design flaw a pattern scanner would pass. Reachability analysis confirms the new dependency's one known CVE sits in a function the code never calls, so it's logged but doesn't block.
- Review with evidence. The developer fixes the missing permission check, and a reviewer approves the PR with the findings and the blocked install attached.
- Keep the record. The audit trail links the original prompt, the agent session, the blocked package, the approved CI change, the review findings, and the merged commit. If an auditor or incident responder asks later, the answer takes minutes, not days.
Notice what did not happen: no one relied on the agent's own assurance that its work was safe, and no late-stage gate held the release for a week.
Where to start: a secure ADLC checklist
Work through these steps in order and measure as you go. Most can be enforced in the development and CI tooling you already run.
- Inventory agents and integrations. Know which coding agents run, who uses them, which tools and MCP servers they connect to, and what they touch.
- Define permissions and approvals. Set least-privilege access per agent, an allowlist of tools and MCP servers, and the actions that always need a human.
- Guard dependency installs. Put a package firewall in front of agent installs.
- Add security context at generation through system prompts, rules files, and IDE guardrails.
- Put security-aware review on every pull request, including agent-authored ones.
- Prioritize findings by reachability so the queue reflects real exploitability.
- Automate safe remediation with patches and vetted upgrade paths.
- Review logs and exceptions regularly, and tighten or relax policies based on what you see.
How to tell whether your ADLC controls work
Good controls lower risk without adding friction developers route around. Set a baseline before you roll out new controls, then track a small set of measures over time.
Pick two measures to report each month: one for engineering leaders and one for security leaders. Read them in the context of your own workflow rather than against a generic benchmark. Numbers turn the program into something you can prove.
FAQs
What is the difference between ADLC and SDLC?
The SDLC describes how software is planned, built, tested, and released. The ADLC is the same lifecycle with AI agents doing much of the work. Agents can run commands, install packages, and act with delegated permissions, so security must govern agent actions as well as verify the code.
Is there a standard number of phases in the ADLC?
No. There is no single official phase list in the ADLC. Teams use models with five to eight stages, and frameworks like NIST SP 800-218A map secure practices onto existing processes. What matters is that every point where an agent acts has a matching control.
Does ADLC mean building AI agents, or using agents to build software?
Both uses exist. "Agentic development lifecycle" usually means AI agents building software, which is what this guide covers. "Agent development lifecycle" means designing and operating AI agents as products. The security controls overlap but are not the same.
How is agentic development different from AI-assisted coding?
AI-assisted coding suggests changes a developer approves one at a time. Agentic development lets the agent act across files, tools, and pipelines, so controls must scale to more output and cover the agent's actions.
What are the main security risks of AI coding agents?
The main risks are insecure code and design flaws produced by default, hallucinated or malicious dependencies pulled in automatically, risky actions taken with inherited permissions, and a gap where output ships faster than review.
Can traditional DevSecOps and SAST tools secure the agentic development lifecycle?
Traditional DevSecOps (automated security checks wired into the CI/CD pipeline) and SAST tools still catch known patterns and CVEs. They miss design flaws, transitive dependencies, and anything an agent does outside the pipeline. Pair them with agent governance, security-aware review, and reachability.
Does securing AI coding agents slow development down?
It doesn't have to. Guardrails at generation, package controls at install time, reachability-based prioritization, and automated remediation cut noise and blocked pull requests, so teams fix what matters while agents keep shipping.
Ship code without compromise
Agentic development is here to stay. The teams that do well will secure the lifecycle at its control points so they keep the speed. Govern what agents can do, stop risky packages before they install, prevent insecure patterns at generation, review every pull request, prioritize by reachability, and remediate without stalling delivery.
See how this maps to your own agents, code, and pipeline. Book a demo.
What's next?
When you're ready to take the next step in securing your software supply chain, here are 3 ways Endor Labs can help: